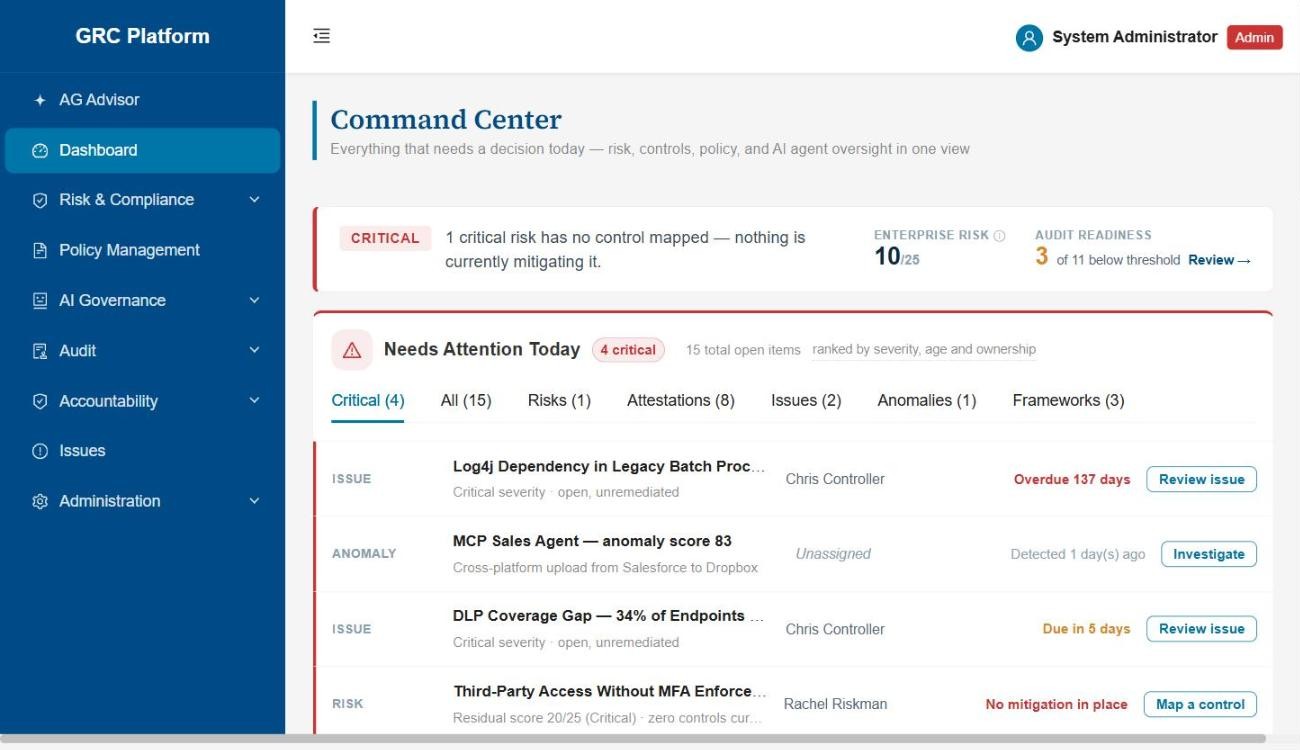
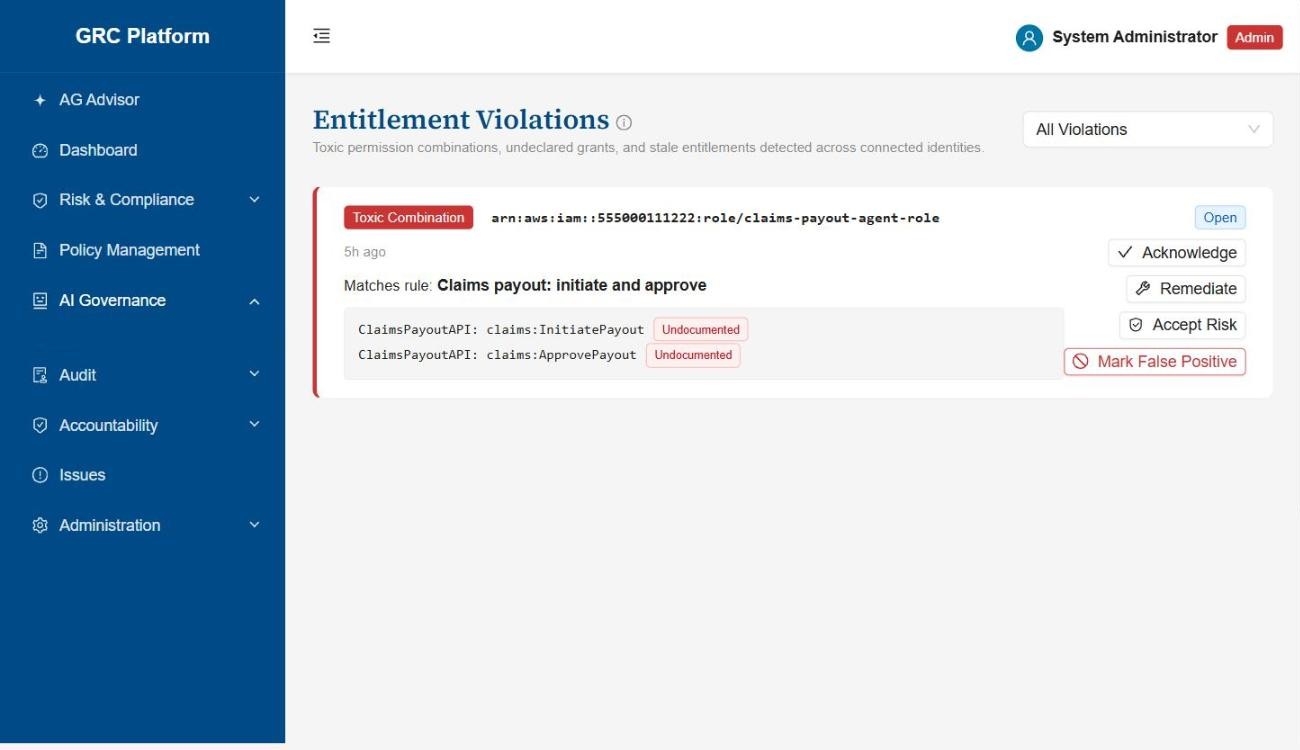
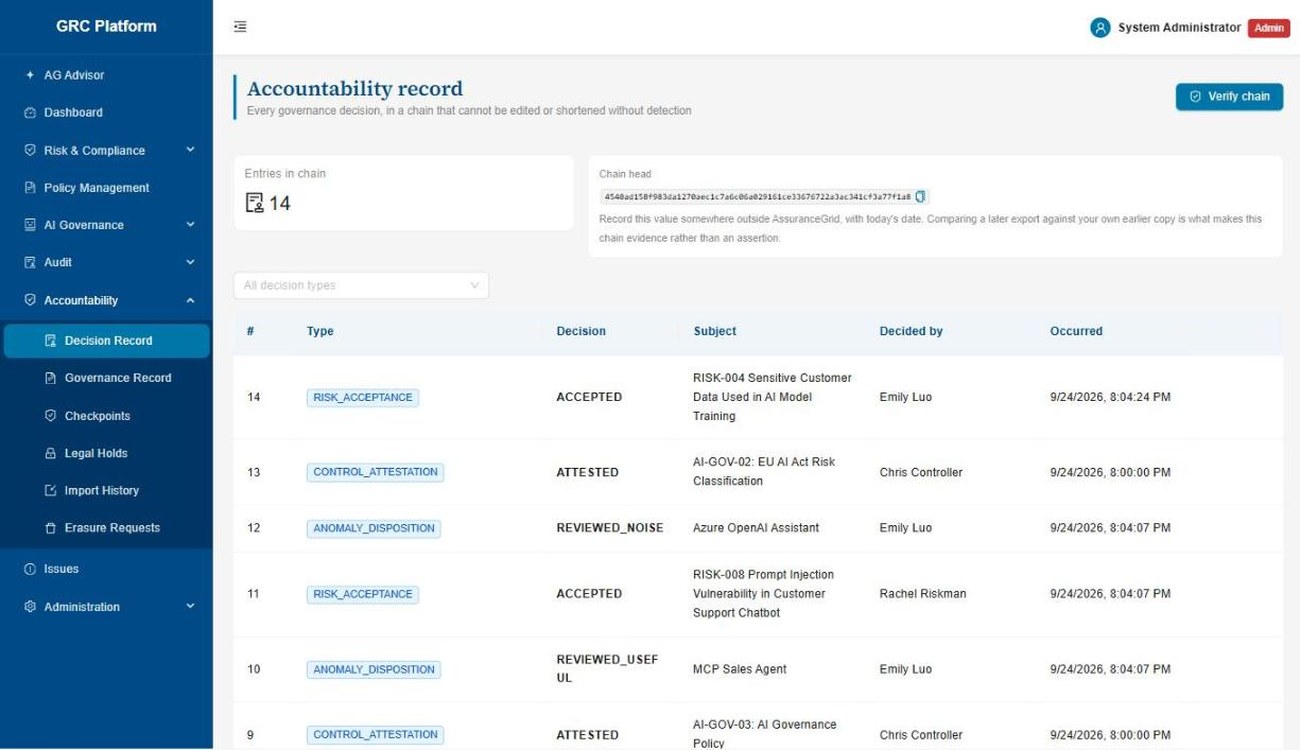
11 frameworks mapped today, on every tier, with more added as they ship
Not another GRC platform.
Not an AI-only point tool either.
Built for teams that answer to an auditor or a regulator and need one system of record for risk, compliance, and the AI agents now acting alongside their people.
Complete GRC
Risk register, control library, attestations, KRI/KCI monitoring, and framework mapping across SOC 2, NIST CSF, SOX, HIPAA, and more: a full system of record, not a checklist.
Human + Agent Accountability
Separation-of-duties checks and a retained, regulator-grade record spanning people and AI agents alike, not an AI-only add-on bolted onto GRC.
Simple & Affordable
Deploy in weeks, not months. No consultants, no dedicated GRC department, and predictable pricing a fraction of legacy platforms.
See pricing →The controls your security team will ask about
A governance platform holds your most sensitive evidence. Here's what protects it, with nothing listed beyond what's actually running today.
AWS Cloud-Native
Fargate containers behind an Application Load Balancer.
Tenant-Isolated Data
Every customer's data is scoped to their own tenant throughout the data layer.
Encrypted in Transit
All traffic served over HTTPS, with TLS terminated at the load balancer.
Role-Based Access
8 roles enforced at the API layer, with real separation of duties.
Full Audit Trail
Every state-changing action logged with actor, timestamp, and before/after values.
Private Networking
The database sits in an isolated subnet with no direct route from the internet.
Governance has changed.
We built for what's next.
Legacy GRC & Checklist Tools
- 6–12 months to deploy, consultant-driven
- AI governance bolted on as a checklist, if at all
- No AI system inventory or risk classification
- High total cost of ownership
- Built around the annual audit cycle
AssuranceGrid
- Deploy in weeks, self-service
- AI governance native from day one
- Every AI system inventoried and risk-classified
- Lower total cost of ownership
- Built for continuous evidence, every day
Help shape the next generation of complete GRC
Selected organizations get free implementation, direct product influence, priority support, and early access to every new capability, in exchange for real-world feedback.
Frequently asked questions
What is AssuranceGrid?
AssuranceGrid is the accountability record for AI agents in regulated firms. It connects what people and agents are authorized to do, what they did, and which control, owner, and obligation that maps to, including a centralized risk register, reusable control library, separation-of-duties analysis across AI agents and non-human identities, evidence and attestation workflows, and compliance framework mapping, so the answer to a regulator or auditor is a record, not a reconstruction.
What compliance frameworks does AssuranceGrid support?
AssuranceGrid lets you manage multiple compliance frameworks without duplicating work. A single control maps to every framework where it applies, dramatically reducing the effort of maintaining them separately. Today that includes SOC 2, NIST CSF, SOX, CMMC L2, ISO 27001, ISO 42001, NIST AI RMF, HIPAA, GDPR, and the EU AI Act, with new frameworks added in days rather than months.
How is AssuranceGrid different from legacy GRC platforms?
Legacy GRC platforms are slow to deploy, consultant-led, and treat AI governance as an afterthought. AssuranceGrid is a self-service platform that ties agent identity, entitlements, and control ownership into one retained record, and it deploys without a consultant engagement.
| Legacy GRC | AssuranceGrid | |
|---|---|---|
| Time to deploy | Months | Weeks |
| Rollout model | Consultant-led | Self-service |
| AI governance | Separate or bolted on | Built in from day one |
| Pricing | Quote on request | Published and predictable |
Does AssuranceGrid help with EU AI Act compliance?
Yes. AssuranceGrid inventories AI systems, classifies them by EU AI Act risk level, and maps required controls alongside your existing compliance frameworks. AssuranceGrid also offers a free 15-question EU AI Act readiness assessment to help organizations understand their current level of preparedness now that enforcement is in effect.
Does AssuranceGrid support ISO 42001?
Yes. ISO/IEC 42001 is the first international standard for an AI management system, and AssuranceGrid maps controls to it alongside NIST AI RMF, SOC 2, and the other frameworks it supports. AssuranceGrid's free Governance Debt Assessment and whitepaper are both built around a model, Operational Trust, designed to align with ISO 42001's requirements directly.
How long does it take to deploy AssuranceGrid?
Most organizations can be up and running in a few weeks using pre-built frameworks and guided onboarding, without consultants or a dedicated GRC department.
Who is AssuranceGrid built for?
AssuranceGrid is designed for organizations with small security or compliance teams that still need to satisfy customers, auditors, and regulators. It's ideal for growing companies that have outgrown spreadsheets but aren't ready for the cost and complexity of traditional enterprise GRC software.
Why does AssuranceGrid include AI governance?
AI introduces governance challenges that traditional GRC software was not designed to address. AssuranceGrid helps organizations inventory AI systems and agents, classify AI risk, define AI governance policies, and map AI controls alongside existing compliance requirements, all in one platform instead of separate tools.
Can AssuranceGrid replace spreadsheets?
Yes. Many organizations manage risk registers, controls, evidence requests, and compliance tracking across multiple spreadsheets. AssuranceGrid centralizes this work in a single risk management platform, making collaboration easier, reducing manual effort, and providing real-time visibility into compliance and AI governance.
Does AssuranceGrid integrate with our existing tools?
Yes. AssuranceGrid includes built-in evidence connectors for GitHub, Okta, BambooHR, and AWS that automatically collect compliance evidence for your controls, reducing manual audit prep. More connectors are added over time.
Does AssuranceGrid support single sign-on (SSO)?
Yes. AssuranceGrid supports OIDC-based single sign-on, configured per organization so your team can log in through your existing identity provider instead of managing separate credentials.
See the platform
Tell us about your team and what you're trying to solve, and we'll walk you through AssuranceGrid live: no canned demo, just your use case.